
Understanding AI Agent Security and Its Implications
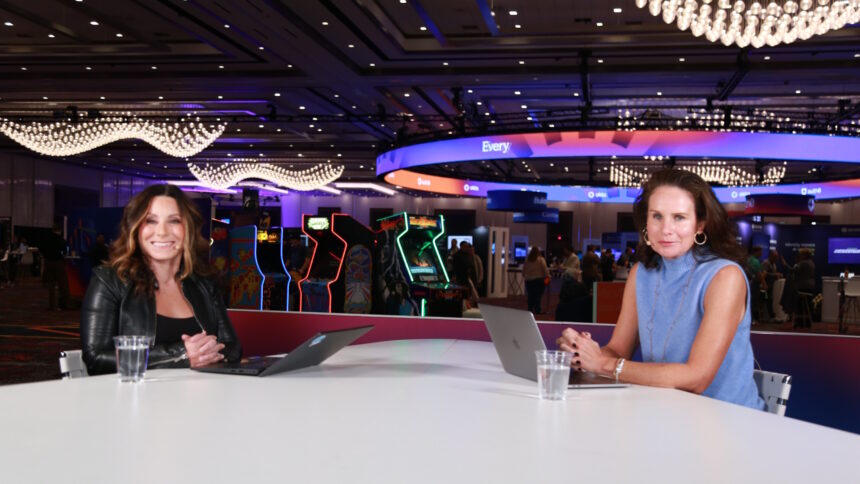
The security of AI agents now hinges on gaining a comprehensive understanding of their capabilities following their access to various systems. These agents can operate across multiple applications, delegate tasks to other agents, and implement changes at a speed that often surpasses the ability of security teams to monitor and review. This reality underscores the urgent need for enhanced visibility and stringent permission limits, along with a crucial inquiry: how can organizations recover from actions already executed by an AI agent? According to Krista Case, principal analyst at theCUBE Research, Okta is actively working on solutions related to the discovery, authorization, and runtime controls of these agents, viewing them as an emerging source of insider risk.
The Need for Recovery Plans in AI Agent Security
Okta has developed an approach that focuses on identifying AI agents, assessing their permissions, monitoring their activities, and responding appropriately when necessary. Case emphasized that this framework extends beyond merely granting initial access. While halting an agent’s operations might prevent any future actions, it does not rectify changes that have already been made or any subsequent tasks that may have been triggered within interconnected systems. “The kill switch revokes authority and prevents the AI agent from taking any future actions,” Case explained. “However, it fails to address prior alterations or downstream effects of its actions.”
This issue is compounded when one agent transfers responsibilities to another. Effective response protocols must identify all impacted systems and work towards restoring a trusted state instead of simply deactivating a single identity. Case highlighted the importance of establishing clear human accountability over the actions of AI agents, suggesting that these entities should not inherit the full spectrum of permissions possessed by their human counterparts. “Who ultimately bears responsibility for the actions of this AI agent?” she queried, stressing that it is critical to ensure a distinction in access levels between human users and their AI counterparts.
The Scale of AI Agents and Oversight Challenges
The sheer volume of AI agents in operational environments is already putting organizational controls to the test. A case study involving a financial asset management company revealed that it had identified roughly 13,000 agents within its network, though only about 1,000 were deemed valid. This statistic indicates that a significant number of agents are being introduced without adherence to established IT protocols, complicating the tracing of authority transfers among users, agents, and applications.
“The sharing of telemetry and fostering interoperability is essential,” she affirmed. “It’s a vital initiative, and I’m eager to see its implementation. However, the challenge will arise when multiple platforms provide differing insights regarding necessary actions. Determining the authority levels within the technological architecture will be critical.”
The evolving landscape of AI agent security presents a formidable challenge for organizations striving to safeguard their information technology ecosystems. As AI becomes increasingly integrated into daily operations, understanding and controlling these agents is imperative for maintaining security and mitigating insider risks. Enhancing visibility, establishing clear ownership, and fostering collaboration among various platforms will be vital steps in navigating the complexities posed by AI agents in cybersecurity.