
In a recent wave of cyberattacks targeting cold storage facilities in Europe, the French national blood service became a victim, with hackers gaining control of medical facility refrigeration systems and raising their temperatures.
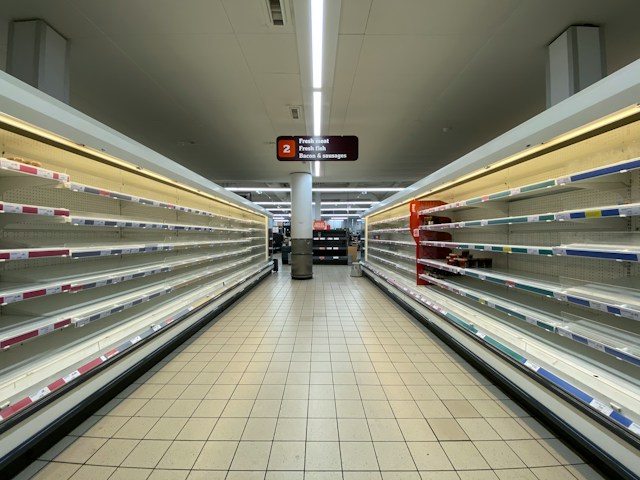
The French Blood Establishment (EFS) reported that, despite the attack, the blood supplies were secured and there was “no loss of blood products.” This incident follows a series of cyber incursions affecting supermarkets across various European nations, resulting in substantial financial losses due to spoiled products.
In October, hackers infiltrated numerous supermarkets in France, causing temperatures in connected refrigeration units to surge to 50 degrees Celsius overnight. Officials have deemed this assault “unprecedented” as food loss and fires ensued at major food retailers. Subsequently, similar attacks spread across the continent, impacting refrigeration systems in the U.K., Italy, and Germany, after disruptions were reported in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands, and Sweden.
“These attacks represent a deliberate effort to disrupt our food supply chain and erode consumer confidence—an alarming situation that warrants serious attention,” stated EU Commissioner for Agriculture Christophe Hansen. “The recurrence of these cyberattacks is extremely troubling.”
While connected refrigeration units offer remote monitoring and control capabilities, they introduce potential vulnerabilities. Cybercriminals can exploit legacy or unpatched refrigeration management systems that may employ default passwords or weak administrative bypasses based on dates.
“Retail is particularly vulnerable due to the extensive networks of refrigeration controllers, building management systems, access panels, and point-of-sale equipment utilized by chains,” remarked Tom Hegel, a cybersecurity expert at SentinelOne, in an interview with Reuters.
As of now, cybersecurity professionals have not definitively identified the perpetrators behind these attacks. Possibilities include Russian hacking groups, Iranian hacktivists, or state-sponsored operatives, but it may also involve individuals conducting costly pranks. Some cybersecurity firms are employing false software as honeypots to collect intelligence on the attackers.