
Post-quantum Regulations Set Deadlines for Cybersecurity Readiness
The evolving landscape of post-quantum regulations is transforming a formerly distant cyber threat into urgent initiatives with concrete timelines. As governments begin to solidify their approaches, organizations operating internationally must navigate varied migration strategies, with many targeting compliance around 2030.
In Australia, a full transition to post-quantum cryptography (PQC) is a priority, while countries in Scandinavia and the Baltic region are generally aligning with European Union directives regarding roadmaps and critical systems. According to Naomi Wynn, CEO of the National Energy Public Key Infrastructure (NEPKI), and Jostein Stokkan, Product Manager for Atea Norge AS, U.S. directives also underline this urgency; for instance, Executive Order 14412 mandates that federal agencies assign leads for PQC migration and advance high-value assets to PQC standards by December 31, 2030.
Wynn emphasized the proactive stance Australia is taking: “We are leading in terms of regulatory measures,” she noted, highlighting the full compliance mandate from the Australian Signals Directorate and the Australian Cyber Security Centre, which calls for complete PQC migration by 2030.
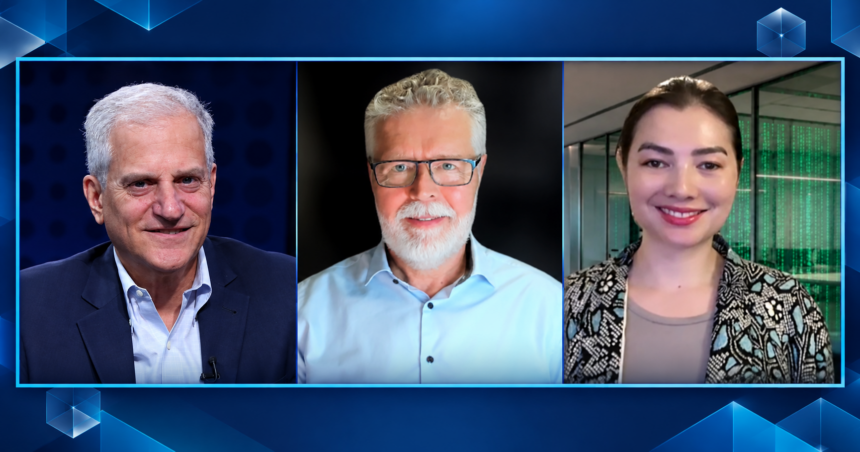
During their discussion at DigiCert’s World Quantum Readiness Day, Wynn and Stokkan shared insights with Dean Coclin, Senior Director and Digital Trust Specialist at DigiCert Inc., on how regional mandates impact their company’s migration strategies and responsibilities. Their conversation was part of an exclusive broadcast on theCUBE, SiliconANGLE Media’s livestreaming platform.
Complexity Arises From Varied Post-quantum Standards
Countries are now developing distinct post-quantum standards, which adds a layer of complexity to compliance beyond simply meeting regulatory deadlines. Organizations functioning across different jurisdictions may find themselves needing to adjust to a variety of algorithms and requirements, as pointed out by Stokkan.
“The conflicting standards will influence PQC,” Stokkan remarked. “However, if we assist businesses in becoming more crypto-agile—capable of adapting to various encryption methods as needed—it will smooth the transition for all involved.”
Despite the accelerating framework from post-quantum regulations, firms are grappling with significant implementation uncertainties. These unresolved questions are expected to shape the next phase of migration efforts, Wynn indicated.
“There is no universal solution, and no one-size-fits-all template exists,” she explained. “Yet, I hope that within a year, we will see better guidance that clarifies expectations and defines what constitutes sufficient compliance.”