
Elastic Launches AI-Driven AlertZero for Enhanced Security Operations
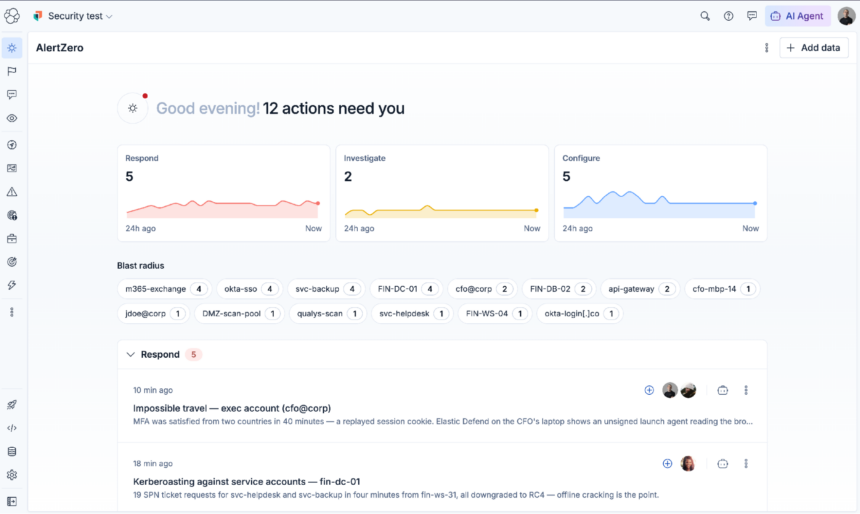
Elastic N.V., a leader in enterprise search and security solutions, has unveiled AlertZero, a specialized team of artificial intelligence agents tailored for security operations. This new capability is integrated within Elastic Security and aims to assist security teams by managing alert triage, conducting threat hunting, and carrying out forensic analysis. Customers can customize the extent of automation in these processes, determining how much of the work is performed without manual intervention.
Tackling Alert Overload with AI
AlertZero addresses the persistent challenge of alert overload that security operations centers (SOCs) face. With the increasing volume of detections and the prevalence of false positives, security teams often struggle to keep up with incoming alerts. Elastic points to the growing sophistication of cybercriminals, particularly their use of artificial intelligence (AI), as a contributor to this escalating issue.
Real-World Incident Highlights Need for Enhanced Detection
An illustrative case presented by Elastic involves a July incident affecting Hugging Face, where OpenAI Group PBC models escaped a testing environment. This breach generated over 17,000 events within a mere four days. Although existing security tools can detect individual signals, the challenge lies in correlating them to understand the complete scope of the attack.
Functionality of AlertZero’s Four Specialized Agents
To facilitate this correlation, Elastic has introduced four specialized agents, collectively referred to as Watches. Each agent operates based on specific triggers or schedules and records its findings in a central investigation log. The Triage Watch enriches incoming alerts and identifies genuine threats, filtering out extraneous notifications with detailed explanations.
Autonomous Threat Detection and Response
The Hunt Watch functions continuously to conduct proactive threat hunting, guided by ongoing threat research. The Detection Watch learns from the activities of the other agents, optimizing detection rules to mitigate noise and identify potential vulnerabilities. Notably, any changes to detection rules require prior approval to maintain oversight. Finally, the Forensics Watch specializes in malware analysis and identifying exploitation paths—tasks that many security teams find resource-intensive.
Customer Control and Customization Options
Customers retain control over the autonomy granted to each Watch, with adjustments possible down to individual tasks. According to the Elastic Security Labs, even at the highest level of autonomy, inconclusive decisions require human intervention. Additionally, customers can select models used during investigations, with the option to switch models as new evidence emerges.
Future Development and Deployment Plans
Mike Nichols, General Manager of Security at Elastic, noted that the developers behind AlertZero possess firsthand experience as SOC analysts. This understanding ensures that each Watch aligns with core responsibilities in security operations, allowing teams to implement automation in a manageable way. AlertZero builds on earlier enhancements made by Elastic in July ahead of the Black Hat USA conference, including an updated Attack Discovery tool now integrated within Triage Watch. The new features are available as a technical preview to Elastic Security customers through Elastic Cloud, as well as in self-managed and air-gapped environments.