
AI-Native Cybersecurity Addresses Evolving Threats
As cyber threats continue to evolve, the need for AI-native cybersecurity is increasingly critical. These sophisticated defenses must adapt swiftly to outpace attackers while ensuring the continuous operation of essential infrastructure. This challenge is uniting security expertise with specialized computing resources, integrating automation into the systems that organizations rely on to train and deploy AI models.
According to Bartley Richardson, Chief of AI at CrowdStrike Holdings Inc., the company recorded its fastest eCrime attacker breakout time at just 27 seconds in 2025. This statistic underscores the urgent need for rapid response capabilities in the face of increasingly agile threats. To combat such challenges, organizations require advanced computing power for both training AI models and executing inference.
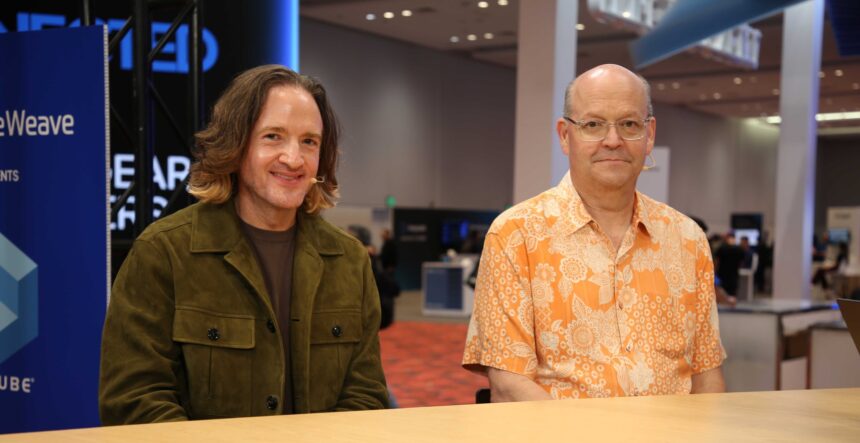
“Human intervention alone isn’t enough to combat these threats,” Richardson remarked. “We need machine-speed defenses, which are fundamentally reliant on robust infrastructure.” In a recent discussion at the Fully Connected event, Richardson, along with Jim Higgins, Chief Information Security Officer of CoreWeave Inc., shared insights with theCUBE Research’s Dave Vellante and John Furrier. They explored topics such as machine-speed defense, infrastructure security, and the importance of operational trust in AI systems.
Transforming Attacks into Training Data
The collaboration between CrowdStrike and CoreWeave aims to merge CrowdStrike’s vast security data and adversarial expertise with CoreWeave’s infrastructure capabilities. CoreWeave provides essential training and inference capacity for CrowdStrike’s SafeMind and acts as a design partner for its Cyber Superintelligence Lab.
“The key concept we are working with is adversarial co-evolution. This involves training our offensive capabilities to navigate around defensive operations while simultaneously training our defensive models on large-scale infrastructures to learn from these simulated attacks,” Richardson explained.
Higgins emphasized the need for CoreWeave to enhance its security measures while maintaining operational efficiency. He referred to this balance as the “aikido of the security problem.” His approach draws from the principle of leveraging ongoing operations to bolster security. “Using AI to review and strengthen my code is essential, as is integrating these safeguards into the continuous integration and continuous delivery pipeline to address misconfigurations dynamically,” said Higgins.
Cybersecurity Must Start with Fundamentals
Despite advancements in AI and cybersecurity, attackers still operate within constraints related to budget and time, often targeting the easiest vulnerabilities. Higgins noted that exploiting multiple standard weaknesses can create significant openings for cybercriminals. “When we claim our systems are secure, it’s vital that we routinely test and verify their integrity, while also adhering to the fundamentals of security hygiene,” he advised, advocating for regular updates and continuous monitoring.
CrowdStrike is making significant investments in automation to enhance its continuous security operations. Richardson stressed the importance of building confidence in these capabilities among both CoreWeave and its client base. “People often ask me when we will reach the endpoint of AI development, and my answer is simple: never. AI will only transition to automation once we trust it,” he said. “As we invest in round-the-clock AI solutions, instilling trust within our systems is paramount.”
To watch the complete video interview featuring Richardson and Higgins, part of SiliconANGLE’s coverage of the Fully Connected event, please visit theCUBE’s channel.