
Post-Quantum Cryptography Transition: A New Approach for Organizations
Organizations are finding it beneficial to approach post-quantum cryptography (PQC) as a migration initiative rather than a complex scientific problem. As the implementation phase of PQC evolves from theoretical discussions to actionable strategies, organizations can assess readiness and strategically plan for unresolved dependencies. This perspective shifts the focus away from viewing quantum technology solely through a physics lens.
Even seemingly simple technical modifications can take years to implement when organizational factors such as budgets, product compatibility, and governance come into play. To ease the transition, organizations are encouraged to conduct practical tests and stages of planning that can clarify the process. Colin Soutar, Managing Director at Deloitte Touche Tohmatsu Ltd., emphasizes that while dealing with PQC might seem daunting, the path forward is relatively clear if broken down into manageable components.
According to Soutar, removing the term “quantum” from the conversation can help demystify the issue. He reflects on the common misconception that one must be a physics expert to navigate the challenges presented by quantum threats. “There is a threat out there in the future, and the steps to mitigate that are generally known,” he states, suggesting that while the transition can be extensive and complex, the foundational steps are relatively straightforward.
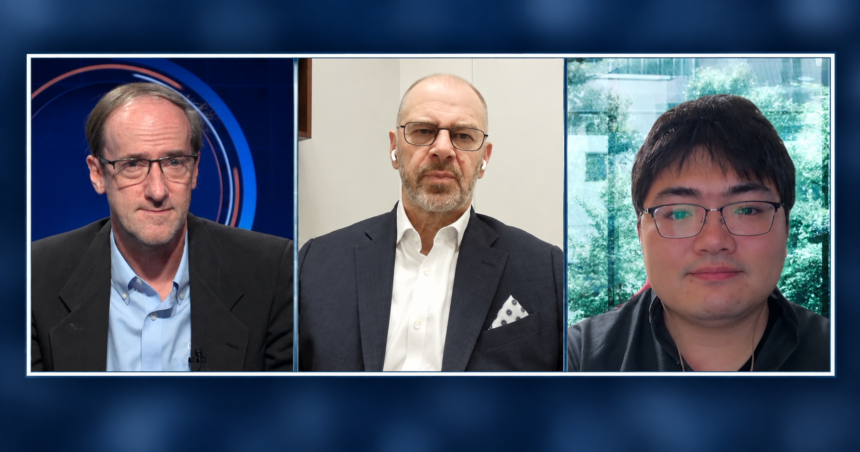
Soutar, along with Sadaaki Yamazaki, Senior Security Specialist at Daiwa Institute of Research Ltd., joined DigiCert Inc.’s Tim Hollebeek for an in-depth discussion during DigiCert’s World Quantum Readiness Day. Their conversation, broadcasted live on theCUBE, explored various strategies for reducing technical ambiguity while adequately acknowledging the extensive requirements for migrating enterprise systems.
Initiating PQC Implementation with Available Technologies
Daiwa Institute of Research conducted a proof of concept utilizing a hybrid model for its online trading system, characteristic of their innovative approach to PQC. Using a post-quantum-enabled load balancer, the organization assessed the performance of Transport Layer Security (TLS) under realistic conditions. Yamazaki noted that, in their evaluations, the average TLS handshake time was only marginally affected, increasing by about 1.2 milliseconds, which had a negligible impact in their high-bandwidth data center. However, he cautioned that organizations operating over wireless networks or in bandwidth-restricted environments should thoroughly evaluate the implications in their specific contexts.
The technical readiness for PQC varies significantly depending on the cryptographic functions in use. The National Institute of Standards and Technology’s Federal Information Processing Standard 203 is one critical element in the phased approach recommended by Yamazaki. He points out that while the allure of a comprehensive rollout is strong, cryptographic elements such as key establishment and digital signature readiness are at different developmental stages. For instance, ML-KEM has already received standardization, while hybrid key exchange methods like X25519MLKEM768 are increasingly available across products and platforms. Implementing these earlier can effectively mitigate the ‘harvest now, decrypt later’ threats.
Governance Challenges Heightened by Enterprise Scale
The complexity of implementing PQC at an enterprise level extends beyond technical obstacles to encompass governance issues as well. While the goal is to develop a complete inventory of cryptographic uses, attempting to do so initially can hinder progress when systems and ownership are extensive and convoluted. Soutar advocates for an iterative approach, recommending that organizations prioritize progress by focusing on their most critical assets and systems rather than striving for a complete inventory from the outset.
Enterprise public key infrastructure interacts with a wide array of applications—including certificates, authentication, code signing, application programming interfaces, virtual private networks, and cloud services—spanning various components of the organization. Yamazaki highlights that successfully navigating the migration challenge involves more than just replacing a single cryptographic algorithm. The main difficulty lies in pinpointing where cryptography is employed, understanding the dependencies involved, and coordinating a comprehensive migration throughout the organization. According to him, the technological aspect is just one facet of the hurdles faced; effective governance and accurate cryptographic inventories are likely to present larger challenges.